Guard Rail Company
Cyber Governance, Risk & Regulatory Advisory
Structured assessments, governance frameworks and regulatory readiness support for organisations operating in Malaysia.
Partner-led delivery
Risk-based prioritisation
Management-ready reporting
18+ Years of Experience
in GRC & Cyber Advisory
Engagement Starts From
RM20,000
Guard Rail Company
Cyber Governance, Risk & Regulatory Advisory
Structured assessments, governance frameworks and regulatory readiness support for organisations operating in Malaysia.
Partner-led delivery
Risk-based prioritisation
Management-ready reporting
Discuss Your
Business Cyber Security Needs
Your enquiry helps our advisory team understand your priorities and discuss a suitable scope.
Business Risk
Do You Know
Where Your Business Is Exposed?
Security tools alone do not show whether your organisation is ready. Unclear responsibilities, untested controls and incomplete evidence leave gaps that surface during audits, regulator reviews and incidents.
Are critical cyber risks identified and prioritised?
Are cybersecurity responsibilities clearly assigned across your organisation?
Can you demonstrate readiness for an audit or a regulator review?
Are personal data, technology vendors and third-party access adequately governed?
A structured assessment establishes your current state and the priorities that follow from it.
Our Services
Our Advisory Services
Governance
Direction, accountability and documented policy for cyber and information security.
Risk
Identification, assessment and treatment of cyber, data and third-party risk.
Compliance
Independent assessment and assurance against regulatory and standards requirements.
AI Governance
Advisory on governance of artificial intelligence adoption, aligned to ISO/IEC 42001, covering AI risk assessment, policy development and management oversight.
Our Services
Our Advisory Services
Guard Rail’s services follow its GRC Service Framework: Governance, Risk and Compliance. Services are delivered as projects, retainers or co-sourced arrangements. This structure matches the Guard Rail capability overview that prospective clients receive on enquiry, so the website and the deck present one framework.
Governance
Direction, accountability and documented policy for cyber and information security.
Risk
Identification, assessment and treatment of cyber, data and third-party risk.
Evidence-based assessment of cyber capability across governance, people, process and technology, reported in a maturity scorecard, gap register and multi-year roadmap.
identification and evaluation of cyber and information risks against risk appetite, aligned to ISO 31000.
Framework and assessments for technology and outsourced service providers supporting critical services or data.
Identification of where personal and confidential data resides, how it moves, and the related privacy and leakage risks.
Compliance
Independent assessment and assurance against regulatory and standards requirements.
AI Governance
Advisory on governance of artificial intelligence adoption, aligned to ISO/IEC 42001, covering AI risk assessment, policy development and management oversight.
Why Guard Rail
Partner-led delivery
A senior practitioner leads the engagement from scoping to reporting, not a leveraged junior team.
Risk-based prioritisation
Findings are ranked by risk and business impact, so remediation effort goes to the gaps that matter first.
Management-ready reporting
Results are written for management and board decisions: exposure, required actions, owners and timelines.
Malaysian regulatory knowledge
Working familiarity with the Cyber Security Act 2024 (Act 854), NACSA Codes of Practice, Bank Negara Malaysia RMiT and the PDPA, applied to your sector's obligations.
Advisory-led delivery
Guard Rail advises and does not sell the technology it recommends. Technical testing and implementation are delivered with disclosed specialist partners where required.
Independence Safeguards
Guard Rail does not audit areas in which it has provided implementation or operational support.
Technical testing vulnerability assessment and penetration testing (VAPT), compromise assessment and red teaming is delivered with technical partners where required.
Where an assurance engagement covers services delivered by Nimbus Cloud or another group company, this is disclosed at scoping and the engagement is structured to preserve independence.
Sector Experience
Supply Chain & Logistics
Financial Services
Healthcare
Telecommunications
Oil & Gas
Supply Chain & Logistics
Financial Services
Healthcare
Telecommunications
Oil & Gas
What Your Business Receives
We turn cybersecurity assessments into clear, actionable plans, helping your business identify risks, strengthen security practices, and track continuous improvement.
Cyber maturity scorecard
A structured assessment of current controls, gaps, risks and maturity.
Prioritised remediation roadmap
Recommended actions ranked by risk, business impact, effort and ownership.
Management and board reporting
Decision-ready summaries of exposure, progress and required management actions.
Governance and evidence records
Agreed policies, control ownership, supporting evidence and corrective-action tracking.
Deliverables depend on the agreed engagement scope.
Deliverables depend on the agreed engagement scope.
How We Work
Assess
Evaluate current controls, regulatory obligations and risk exposure.
Prioritise
Identify gaps, rank remediation actions and agree responsibilities.
Remediate
Support governance improvements and coordinate specialist implementation where required.
Validate
Review progress, assess supporting evidence and report residual gaps.
The scope and delivery schedule are tailored to your organisation. Technical testing and implementation involve relevant partners where required
Start with the Support Your Business Needs
Project-Based
Defined assessments, ISMS implementation or readiness work.
Retainer
Ongoing vCISO, DPO or compliance operations support.
Co-Sourced
Work alongside your team on technology, regulatory or ISMS internal audit.
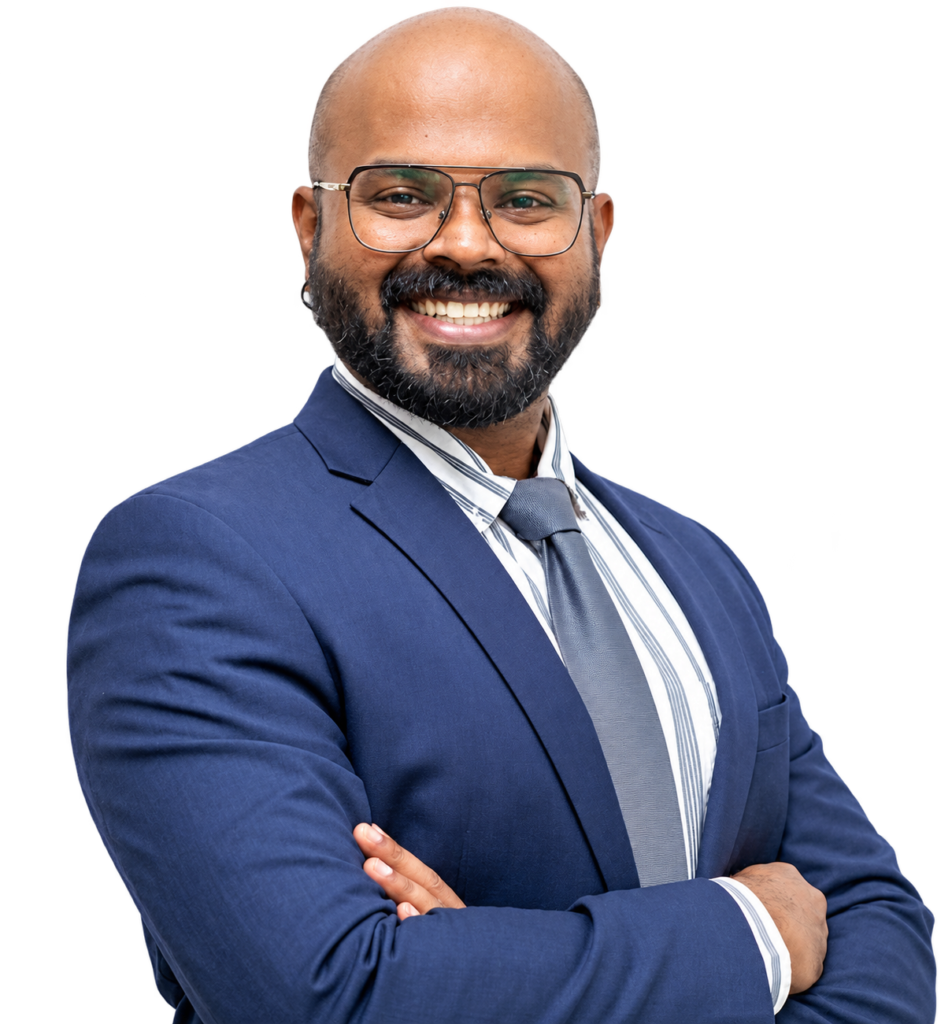
Advisory Led by Experience
Partner · Cyber Governance & Risk Advisory
MKJ’s background spans a Big Four professional services firm, a national applied research and development agency, a Malaysian banking group and the national 5G network company with sector experience across government and government-linked companies, financial services, telecommunications, supply chain and logistics, healthcare, and oil and gas.
Professional credentials:
• Certified Information Security Manager (CISM) — ISACA
• Certified Enterprise Risk Manager, ISO 31000:2018
• Artificial Intelligence Governance, Risk & Compliance, ISO/IEC 42001:2023
Frequently Asked Questions (FAQ)
Make Your Next Cyber Security
Decision with Clarity
Identify your priority gaps and discuss a practical plan to secure the business.